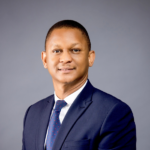
Seen Here: Kudakwashe Charandura, SNG Grant Thornton’s Cyber Advisory Service Line Leader, emphasised the importance of proactive cybersecurity governance, urging boards to make cyber risk a continuous oversight priority rather than waiting for an incident to occur. Photo Credit: Sourced
South African businesses must move beyond treating cybersecurity as an IT concern and embrace it as a boardroom priority, with accountable leadership, proactive preparedness and cross-industry collaboration emerging as critical to surviving an increasingly interconnected digital world.
As artificial intelligence (AI) accelerates digital transformation and the boundaries between information technology (IT), operational technology (OT) and the Internet of Things (IoT) continue to blur, cybersecurity is becoming one of the most pressing business risks facing South African organisations.
That was the defining message at the SNG Grant Thornton South Africa Cybersecurity Summit, hosted and sponsored by MTN, where business executives, risk specialists and technology leaders explored the growing complexity of cyber threats and the urgent need to rethink how organisations approach digital risk.
Held under the theme The Converged Enterprise: Navigating Risk as IT, OT, IoT and AI Converge, the summit challenged traditional perceptions of cybersecurity, positioning it not simply as a technical function but as a fundamental business responsibility with far-reaching consequences for operational continuity, financial performance, reputation and customer trust.
The message was unequivocal: cybersecurity must move into the boardroom.
In his closing reflections, Oupa Mbokodo, Managing Director of Advisory Services at SNG Grant Thornton, emphasised that organisations cannot realistically expect to prevent every cyber incident. Their ability to withstand disruption, respond decisively and recover effectively, however, will increasingly determine their long-term resilience.
He identified preparedness and trust as essential foundations of a resilient organisation, calling on businesses to elevate cyber risk discussions to board and executive level, where strategic priorities, investment decisions and organisational risk appetite are determined.
AI is reshaping the cybersecurity battlefield
The growing adoption of artificial intelligence is adding another layer of complexity to an already challenging cybersecurity environment.
While AI offers significant opportunities to improve productivity, efficiency and innovation, its rapid integration into the workplace is creating new governance challenges. Employees are increasingly adopting AI tools outside established organisational frameworks, potentially exposing businesses to data privacy, security and compliance risks.
At the same time, AI is changing the economics of cybercrime, enabling less experienced criminals to access more sophisticated capabilities and increasing the scale and complexity of potential attacks.
Dominic White, Managing Director of Orange Cyberdefense, examined how AI is transforming the capabilities of both cybercriminals and security professionals. His contribution underscored the importance of keeping pace with emerging threats while ensuring that organisations do not lose sight of the opportunities that AI can unlock.
The challenge for business leaders is therefore not simply whether to adopt AI, but how to do so responsibly, securely and with appropriate oversight.
Boards must stop waiting for a cyberattack
A recurring theme throughout the summit was the need for a fundamental shift in how organisations assign responsibility for cybersecurity.
As IT, OT, IoT and AI become increasingly interconnected, vulnerabilities in one part of an organisation can quickly affect its wider operations. Traditional approaches that leave cybersecurity largely in the hands of IT departments are no longer sufficient.
Kudakwashe Charandura, SNG Grant Thornton’s Cyber Advisory Service Line Leader, stressed that effective cybersecurity starts with leadership and the culture established by those at the top.
Speaking during an executive panel discussion on governance and accountability, he challenged boards to understand their organisations’ cyber exposure and make cybersecurity a standing item on their oversight agendas, rather than treating it as an issue that only demands attention after an attack.
“Don’t ask questions when an attack occurs. Start asking questions as you go,” he urged.
His message highlighted the importance of sustained investment, ongoing engagement and a culture in which cybersecurity is recognised as everyone’s responsibility.
Drawing parallels with routine fire drills, Charandura argued that organisations should adopt similar preparedness practices for cyber incidents. Employees need to understand their responsibilities, leadership teams must know how to respond, and organisations should create environments where people can report concerns without fear of blame.
The emphasis is shifting from reactive crisis management to continuous readiness.
Simulating a cyberattack before reality strikes
The importance of preparedness became particularly evident during an interactive cyberattack simulation led by Vijay Rathour, Partner and Head of Cyber and Digital Investigations at Grant Thornton in London.
Drawing on his experience supporting organisations through major cyber incidents and data breaches, Rathour placed summit attendees in the middle of a fictional unfolding cyber crisis, challenging them to make decisions as the situation escalated.
The exercise exposed the difficult realities organisations face when a cyber incident threatens business operations, sensitive information and customer confidence simultaneously.
It also demonstrated that even the most sophisticated technical security measures cannot guarantee an effective response.
When an attack occurs, organisations need more than technology. They need decisive leadership, clearly defined responsibilities, tested incident response plans and effective communication strategies.
Rathour reinforced the value of conducting regular cyber simulations, explaining how these exercises can reveal weaknesses in decision-making, coordination and crisis communication before a real incident exposes them at potentially significant financial and reputational cost.
Cyber resilience is an ecosystem responsibility
While much of the discussion focused on the risks facing individual organisations, the summit also examined the broader implications of cybersecurity for South Africa’s interconnected economy.
In his opening keynote, Lincoln Mali, CEO of Lesaka Technologies, illustrated the far-reaching consequences of digital disruption through the example of a spaza shop owner whose livelihood depends on an interconnected network of payment systems, financial services and technology providers.
For small businesses operating with limited financial resources, a disruption to these essential services can have devastating consequences.
The example brought home an important reality: cyber resilience is not only about protecting large corporations. It is also about safeguarding the smaller businesses, suppliers and service providers whose operations depend on the same digital ecosystem.
Emily Manganyi, Chief Information Security Officer at the JSE, reinforced this point, arguing that protecting individual organisations is insufficient when businesses are so closely connected through shared systems, services and infrastructure.
She called for stronger collaboration across industries, particularly in supporting smaller and less-resourced organisations that may lack the expertise and financial capacity to defend themselves against increasingly sophisticated threats.
Her message highlighted the need for a collective approach to cybersecurity, recognising that weaknesses in one part of the ecosystem can create vulnerabilities for everyone.
From awareness to action
Closing the summit, Mbokodo urged delegates to move beyond discussions and translate the insights gained into meaningful organisational change.
He challenged attendees to identify at least one practical action they would implement to strengthen cyber resilience within their organisations, reinforcing the idea that progress depends on decisions and behaviours, not simply awareness.
Ultimately, the summit delivered a clear message for South African business: cybersecurity can no longer be viewed as an isolated technology investment or a responsibility delegated exclusively to technical teams.
As AI adoption accelerates and IT, OT and IoT systems become increasingly interconnected, the consequences of cyber incidents will extend further into business operations, economic activity and society.
The organisations best positioned to navigate this evolving landscape will be those that place cybersecurity firmly on the boardroom agenda, invest in preparedness, develop a culture of shared accountability and build stronger relationships across the ecosystems in which they operate.
In an era where digital trust underpins business continuity and economic participation, resilience will not be measured by an organisation’s ability to avoid every attack, but by how effectively it anticipates, withstands and recovers from disruption.
The challenge now is for South African business leaders to turn that understanding into action — before a cyber crisis makes the decision for them.
#Cybersecurity #CyberResilience #SNGGrantThornton #CyberSecuritySummit #DigitalTransformation #CyberRisk #CorporateGovernance #BoardroomLeadership #ArtificialIntelligence #RiskManagement #DigitalTrust #MTN #SouthAfrica